dr.chaos

~/authors/aamir-lakhani

Aamir Lakhani

Founder · Dr. Chaos

Aamir Lakhani is a leading senior security strategist responsible for providing IT security solutions to major enterprises and government organizations. He creates technical security strategies and leads security implementation projects for Fortune 500 companies, and has designed offensive counter-defense measures for the Department of Defense and national intelligence agencies.

His areas of expertise include adversarial AI, cyber defense, mobile application threats, malware management, Advanced Persistent Threat (APT) research, and the dark web. He is the author or contributor of several books, and has appeared on FOX Business News, National Public Radio, and other media outlets as an expert on cybersecurity.

Writing under the pseudonym Dr. Chaos, he operates this blog. In its list of 46 Federal Technology Experts to Follow on Twitter, Forbes described Aamir Lakhani as "a blogger, InfoSec specialist, super hero…and all around good guy."

~/articles

Articles by Aamir Lakhani

210 published articles

Understanding Rainbow Tables

On the topic of breaking passwords, I often hear security professionals and a few other folks mention Rainbow Tables. I used to think a Rainbow Table was a set of pre-computed (pre-calculated) hashes from passwords…essentially a lookup table where a plaintext’s unencrypted password corresponds to a

Aamir Lakhani4 min read

Arachni Web Application Security Framework

Arachni Web Application Security Framework is an open-source Web application scanner and vulnerability penetration testing tool. Unlike many other system scanners, Aracni specializes in finding Web application vulnerabilities. Steps for Installing Arachni on Kali Linux SystemsFirst we will download

Aamir Lakhani2 min read

The Art of Ransomware

Ransomware may potentially be the biggest threat in 2016. Criminal organizations are making big money from ransomware. According to a Geek.com article by Lee Mathews, Cryptowall, a ransomware application, generated over $30 million USD for criminals. People simply pay to get their data back, a syste

Aamir Lakhani4 min read

When Baby Monitors Are a Model For IoT Security

There are several baby monitors that have come on the market recently with remote viewing capabilities, motion detection, and temperature sensors. These are great tools that give parents peace of mind, but with the proliferation of the Internet of Things and manufactures designing products for funct

Aamir Lakhani4 min read

Why I can’t win from a claw machine (and neither can you)

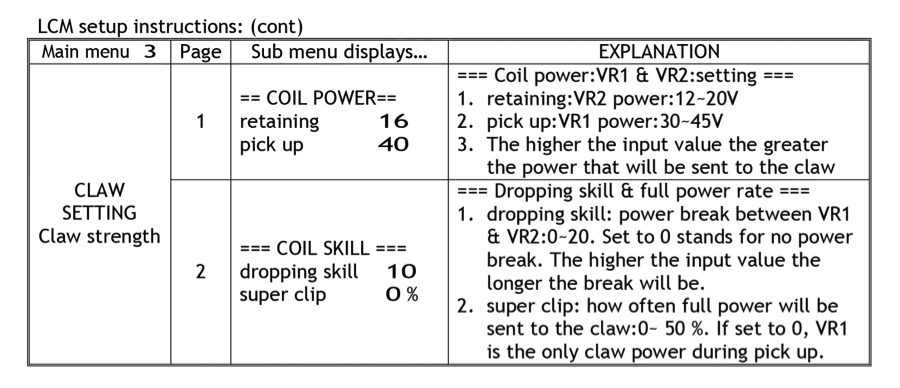
You’ve seen them. They are the cranes we use to try to snatch prizes, commonly referred to as claw machines. They are found in arcades, restaurants, and other establishments. Sometimes they have valuable prizes, and other times….not so much. In either case it is easy to get addicted to them. You thr

Aamir Lakhani4 min read

Mitre ATT&CK Con

We just got back from Mitre ATT&CK Con. Tony G and Dr. Chaos were both impressed. Let's talk about creating and testing the ATT&CK framework.

Aamir Lakhani1 min read

Don't Jack my Crypto

Tony G and Dr. Chaos discuss crypojacking - is it really a problem? How does it lead to greater security threats? What does it really mean for enterprise organizations? Join us for the Dr. Chaos podcast

Aamir Lakhani1 min read

MITRE and RUNDLL

Aamir Lakhani and Tony G talk around MITRE ATT&CK methodology and malware embedded in DLL

Aamir Lakhani1 min read

Crypto Botnets

Aamir Lakhani and "Tony G" discuss the latest techniques in new botnets with hive like awareness.

Aamir Lakhani1 min read

Dr. Chaos Podcast - CryptoJacking

Is CryptoJacking really that bad? What about sites that are asking for user's permission before they mine? Tony G and Dr. Chaos discuss CryptoJacking.

Aamir Lakhani1 min read

Hunting the Hunter

Organizations of all sizes continue to be targets of cyber criminals and the threats that they present. However, some organizations are taking a proactive approach and are hunting for these threats. But what exactly is “threat hunting"? How does it fit into the SOC? Should my organization be threat

Aamir Lakhani1 min read